

On this page
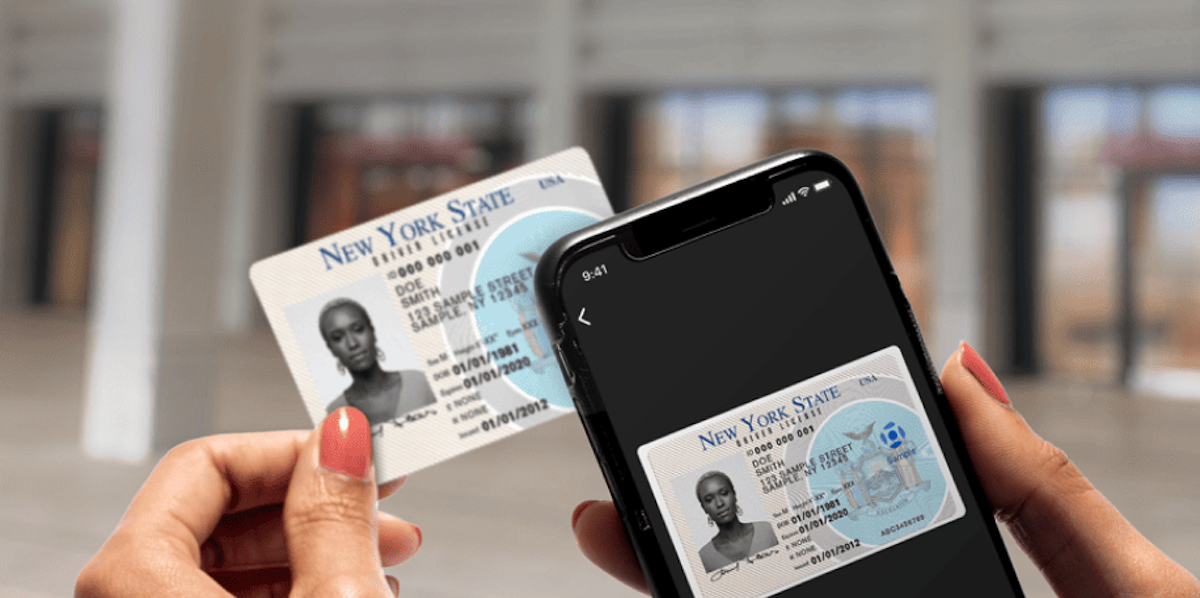
Car-buying has become more seamless than ever. "Frictionless," as the consultants like to say, thanks to modern technology – but thesame tech that makes it easier than ever for customers to take a snapshot of an ID or insurance card or pay stub and get the dealdone can inadvertently lead to violations of the Federal Trade Commission's (FTC) Safeguards Rule and other privacy regulations ...and those regulations have teeth.
The new data privacy guidelines that went into effect in June, 2023 allow the FTC impose penalties of more than $50,000 per day.
And those fines? They're far from theoretical. "Dealers are being fined by the Attorneys General," explains Tom Kilne, a complianceand risk mitigation expert who specializes in the auto industry. "Enforcement on the rise from the Consumer Financial ProtectionBureau (CFPB)."
How can you make sure your staff is staying on the right side of the data privacy regulations while still doing everything they can toclose the deal? Start with the basics:
FTC Safeguards Rule Overview
The FTC Safeguards Rule is a crucial component of the Gramm-Leach-Bliley Act (GLBA) that requires financial institutions, includingcar dealerships that provide financing or leasing services, to implement safeguards to protect customer information.
And, as before, this includes the collection, use, and sharing of personally identifiable information (PII). Violations of the SafeguardsRule can result in significant financial penalties (not to mention a boatload of bad publicity).
Problems With Personal Phones
When salespeople use their personal mobile devices to quickly communicate with customers and collect personal information, severalprivacy breaches can happen almost at once, including:
Lack of Encryption: Personal phones may not have the same level of encryption and security measures as company-provided devices.This increases the risk of unauthorized access and data breaches.
Loss of Control: Dealerships may have less control over the security measures applied to personal phones, potentially leavingcustomer data vulnerable.
Data Storage: Sensitive customer data may be stored on personal devices, raising concerns about data retention, deletion, andpotential exposure if the phone is lost or stolen.
Even when salespeople are careful to delete the PII they collect on their personal phones, issues related to controlling and sharingcustomer data might still arise from:
Third-Party Apps: Salespeople might use unencrypted third-party communication apps like SMS messengers, WeChat, or Facebookto interact with customers, potentially exposing the dealership to additional security risks and data privacy violations.
Unintended Sharing: other apps on your sales staff's phones might lead to the inadvertent sharing of customer data with unintendedparties (example: photos taken or received of documents containing PII may be automatically "backed up," or copied onto iCloud orGoogle Photos) violating privacy regulations.
Ensuring compliance with privacy regulations hinges on transparency and customer consent – and, simply put, customers can'tconsent to unintentional, or even unknown data sharing.
That notion of consent is critical, and requires educating customers to they are thoroughly apprised of the utilization and sharing oftheir data when engaging with your store. Additionally, providing opt-out alternatives becomes imperative, empowering customers todecline the sharing of sensitive information through personal devices and opt for more secure communication avenues.
It's Not Bad News
Embracing the modern convenience of utilizing personal phones for customer interactions within America's car dealerships may bedoing more harm than good, but it reveals a golden opportunity.
The journey toward compliance with the FTC Safeguards Rule and other privacy regulations involves a thoughtful exploration of datasecurity, transmission, and storage strategies that, if followed, could make dealerships a champion customer data privacy. A proactiveapproach to compliance can shield customers from avoidable risks and also elevate their reputation.
Think of data regulations as a prescription for getting your data in order, so that you can more fully understand the true lifetime value ofyour customers, build more trust, and make more money ... which we'll start to explore in part 2.
ORIGINAL CONTENT FROM BRAIN+TRUST.